PHP issues emergency patch for critical flaw found with AI
Maintainers of the language behind most of the web’s server code brought forward a critical patch by a day, as security firms warned that attackers could weaponise it…

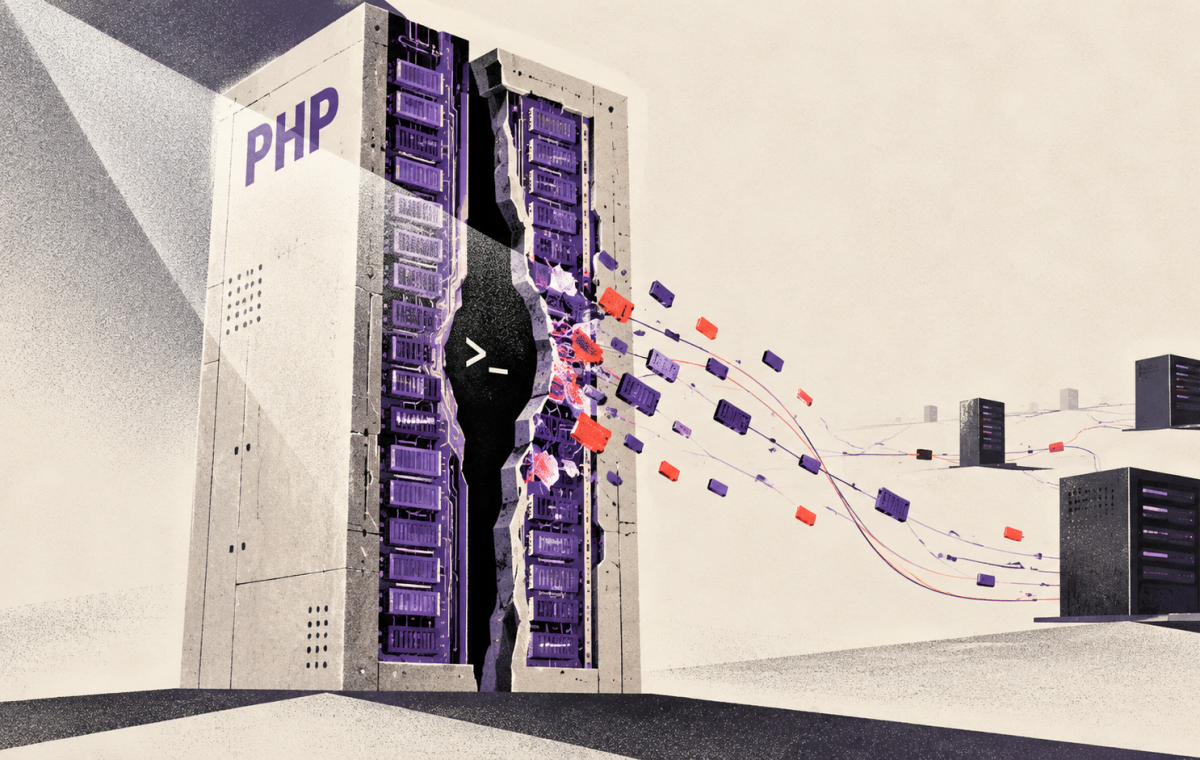
Maintainers of the language behind most of the web’s server code brought forward a critical patch by a day, as security firms warned that attackers could weaponise it within minutes.
The maintainers of PHP, the programming language that runs on a large share of the world’s web servers, released emergency updates on Wednesday for two critical vulnerabilities that can let an attacker seize control of a server without logging in. The fixes shipped on 21 October in PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35, and the project says updating is the only safe option.
The release came a day earlier than planned. Details of the flaws, collectively known as PHP2Shell, leaked onto Hacker News on Tuesday, according to The Wall Street Journal, forcing the PHP security team to warn administrators to expect an urgent update. In an advance notice, the team said it would publish at 14:00 UTC on Wednesday, and it had reserved the right to move faster if details became public or exploitation appeared in the wild.
The stakes are unusually high. PHP underpins as much as 70 per cent of websites, by the Journal’s estimate, including those built on popular content management systems. Because the weakness sits in the PHP runtime itself, its reach extends beyond any single application. Volker Dusch, a security engineer at the nonprofit foundation that oversees PHP, told the Journal it was the project’s most serious security problem in over a decade, and compared it to Heartbleed, the 2014 flaw that sent administrators worldwide scrambling to protect their servers.
The two bugs are rated 9.2 out of 10 on the CVSS v4.0 scale, though the security firm watchTowr scored the issue a maximum 10.0. One involves memory corruption under out-of-memory conditions; the other stems from stale global state. Both concern how PHP manages memory, a class of problem that a researcher had flagged long ago but which was considered too hard to exploit and largely forgotten, according to Thai Duong, chief executive of Calif, the security company that first identified it.
That assumption no longer held once artificial intelligence was applied. Ryan Austin, a Calif researcher, uncovered the flaws in August while auditing PHP’s source code with GPT-5.6 Sol, one of OpenAI’s most advanced models, the Journal reported. OpenAI funded the audit as part of a wider programme to help open-source projects deal with bugs that AI systems are now surfacing in large numbers. Austin found he could take control of code running in a server’s memory with a few dozen requests; on smaller systems the attack takes seconds.
Calif alerted PHP on 11 August. An informal group of researchers, software distributors and security companies then worked in secret on a fix. Researchers at Wiz, the cybersecurity company owned by Google, independently produced further exploits, and OpenAI’s own team contributed findings. The resulting patch touches nearly 200 files and more than 10,000 lines of code. Ami Luttwak, Wiz’s co-founder, told the Journal the flaw was probably too complex to have been found without AI. Accounts of who deserves credit vary: some summaries name Wiz as the discoverer, while the Journal attributes the original finding to Calif.
The concern now is speed. Once patches are public, attackers can compare old and new code to locate the weakness, and AI tools compress that work from days to hours. Duong warned that anyone could feed the patches to an AI system and post a working exploit, adding: “All hell will break loose.” Sansec, another security firm, said it expected “mass attacks to start within 15 minutes of the release”.
Evidence on exploitation is mixed. Cloudflare reported early signs of attacks before the patch was released and deployed temporary firewall rules as a stopgap. WatchTowr and Huntress said earlier that they had seen no exploitation in the wild. A proof-of-concept exploit appeared online on Wednesday morning, though its validity had not been confirmed.
Some organisations chose not to wait. Wikimedia disabled its Phabricator development platform as a precaution hours before the patch landed, and the Journal reported that other administrators were taking sites offline pre-emptively.
The longer-term exposure lies with older installations. No patches have been issued for PHP 5 or PHP 7, branches that are no longer supported but remain common on legacy and shared hosting. A public research repository notes that the main demonstrated attack relies on PHP’s session upload progress feature, which is switched on by default, suggesting a configuration change may offer partial protection for servers that cannot yet be upgraded. Whether that holds across every attack path described so far has not been confirmed by the PHP project.
Written by the newsroom, not a summariser. Free, and you can leave whenever.

0 comments
Anyone can read the thread · subscribers can post